Writing / technology governance
DPDP Compliance Starts at the Mall Entrance
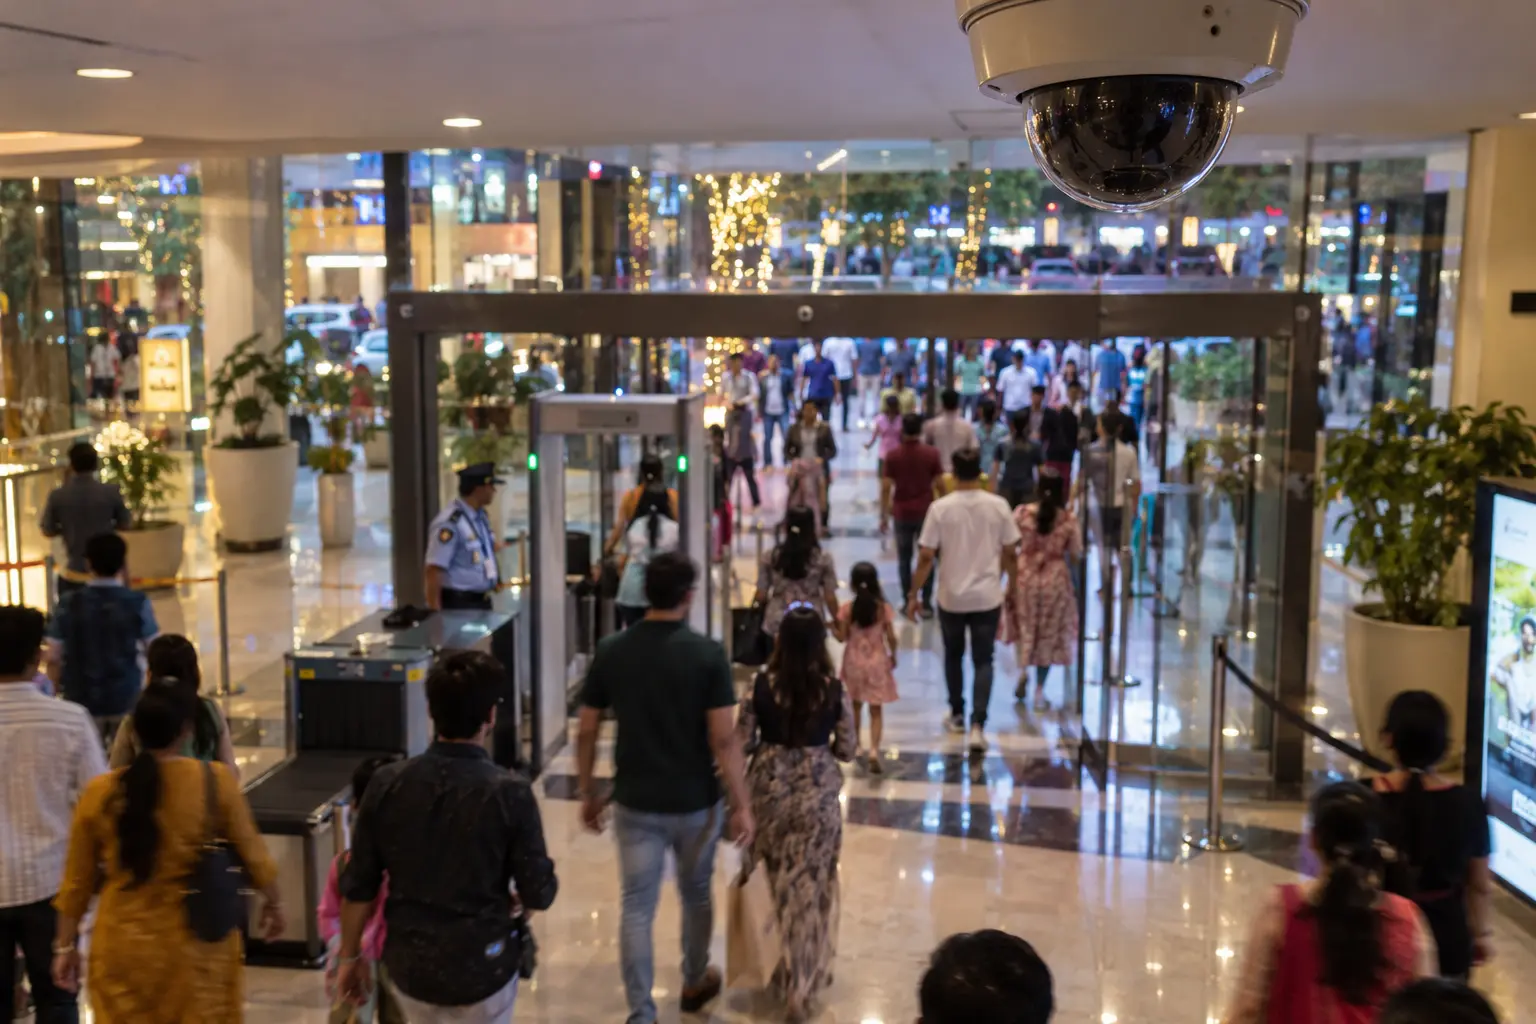
Ask a mall operator where its personal data lives and the first answer is usually the loyalty programme or the billing system. The more honest answer is the building. A shopper can give up a phone number to the Wi-Fi login, a face to the cameras and a vehicle number to the parking gate before walking into a single store.
My view is that physical retailers will find DPDP harder than online businesses, for one reason. In a website, personal data enters through forms that the technology team designed. In a mall, it enters through equipment that facilities, security and marketing teams bought, often from different vendors, often without thinking of it as a data system.
The Digital Personal Data Protection Rules, 2025 give organisations 18 months from November 2025 to comply with their core obligations. This piece is for CIOs, CTOs and operations heads in malls, large-format retail and multi-site stores. It shows where to look first and what to decide before buying any compliance tool.
The short version
Physical retail collects personal data through building infrastructure that IT often does not own. The fastest route to DPDP readiness is to list every device that identifies a person, then remove collection you do not need. Tools come after the map, not before.
- List every device that captures something identifying a person.
- Ask whether each collection is needed at all.
- Assign one owner per data flow, across facilities and IT.
- Settle CCTV retention with counsel before May 2027.
- Clarify who is responsible when tenants and vendors collect data.
- Build breach intake that reaches the right people within hours.
This article sits inside the technology governance cluster, where the wider argument is set out in full.
Personal data enters through facilities
A useful first exercise is a walk, not a workshop. Start at the car park and follow a shopper through the building, noting every point where a device records something that could identify them.
In most malls and large stores that walk finds the same list:
- Parking systems that read or record vehicle numbers.
- Guest Wi-Fi that asks for a mobile number and sends a one-time password.
- CCTV across entrances, corridors, stores and car parks.
- Loyalty, gift card and feedback desks, including QR-code forms.
- Event and contest registrations run by marketing agencies.
- Visitor management at office towers or service entrances.
- Tenant systems, from point-of-sale to delivery apps, that sit on or near the landlord's network.
Each of these is a data flow with a purpose, a retention period and a vendor. Most of them have never been documented that way.
The DPDP Rules require a standalone consent notice that explains the specific purpose in clear language, reasonable security safeguards, prompt breach notification and erasure once the purpose is served. Those obligations apply to each flow on that list where the data is digital and identifies a person. This article is general information, not legal advice; confirm how the law applies to your premises with counsel.
Collect less before you protect more
The cheapest personal data to protect is the data you never collect. Before designing consent screens, ask of every flow on the list: does the business need this at all?
Guest Wi-Fi is the clearest test. Many malls collect a phone number because the captive portal was configured that way years ago, not because anyone uses the number. If the number is only there to send a password, you are taking on consent, security, breach and erasure duties for a login step. Options range from a simpler access method to a clearly separate, optional marketing consent. Which one fits depends on your legal advice and any telecom obligations that apply to public Wi-Fi, so check those before changing anything.
The same question applies to feedback forms that ask for a date of birth, or contests that ask for more than a contact number. Deleting a field is a one-day change. Protecting it is a permanent cost.
Should your organisation do this now?
- Yes, if any form or portal collects fields nobody can name a use for.
- Not yet, if you have not finished the device walk.
- Instead, first: complete the list of collection points.
- Measure it by: number of personal data fields removed at source.
The CCTV retention question
CCTV is where physical retail differs most from online business, and where I would take legal advice early.
Two parts of the Rules pull in different directions. The Rules require personal data to be erased once its purpose is served. They also set a minimum of one year for retaining personal data, associated traffic data and logs of processing, for specified purposes such as investigating incidents. Many malls today overwrite footage after a few weeks because storage is expensive.
The question to put to counsel is specific: does the one-year minimum apply to your camera footage itself, or to logs of how that footage was accessed and processed? The answer changes storage costs, access control design and vendor contracts. Whatever the answer, access to footage should be logged by person and purpose, because that log is what you will need if footage is ever misused.
Risk: a camera system with shared logins and no access log is a breach you cannot investigate.
Should your organisation do this now?
- Yes, if your NVRs or video management system use shared accounts.
- Not yet, if you do not yet know how many cameras and recorders you run.
- Instead, first: inventory recorders, storage periods and vendors.
- Measure it by: share of footage access events tied to a named user.
Tenants and vendors
A mall is a landlord to dozens of businesses, each of which may be responsible for its own customers' data. The landlord's job is to be clear about where its responsibility stops.
Three situations need written answers. When a tenant's point-of-sale runs on the mall's network, whose security obligation covers it? When a marketing agency runs a contest for the mall, the mall is likely the one deciding the purpose, which puts the obligation on the mall even though the agency holds the data. When a parking or Wi-Fi vendor stores data in its own cloud, the contract must require the security safeguards the Rules expect and access to logs when something goes wrong.
My recommendation is to treat every vendor that touches shopper data as part of your own data map, with a named internal owner, rather than as someone else's problem.
A data map you can finish
Large DPDP programmes stall because the first phase tries to map everything. For a physical retailer, a narrower sequence works better.
- Step 1. Complete the device walk and list every collection point.
- Step 2. For each point, record purpose, fields, storage location, retention period, vendor and internal owner.
- Step 3. Remove fields and flows with no purpose.
- Step 4. Write the consent notice for what remains, in plain language, and test it on a phone screen.
- Step 5. Put access logging and retention rules on every system that stores personal data.
- Step 6. Connect breach intake to the same process your security team uses for other incidents.
Only after step 6 is it worth evaluating consent or privacy platforms, because only then do you know what they must connect to.
Before you approve it
Checklist:
- Device walk completed for every property.
- Data map with an owner for each flow, including facilities systems.
- Unnecessary collection removed at source.
- CCTV retention position agreed with counsel and written down.
- Vendor and agency contracts updated for security and log access.
- Consent notices tested on mobile screens.
- Breach intake linked to incident response.
Questions to ask:
- Your team: which systems collecting personal data are managed outside IT?
- Your team: who can view CCTV footage today, and is that logged?
- Your vendor: where is our shoppers' data stored, and for how long?
- Your vendor: how fast can you tell us if our data is exposed?
- Your counsel: does the one-year minimum apply to footage, logs or both?
- Your board: which property is least ready, and what is the plan?
How to measure it
- Mapped collection points. Share of known devices and forms with a documented owner and purpose. Baseline: first walk. Owner: CIO. Review: monthly. Leading.
- Fields removed. Personal data fields deleted at source. Baseline: first map. Owner: data protection lead. Review: quarterly. Leading.
- Named access to footage. Share of CCTV access events tied to an individual. Baseline: current logs. Owner: security head. Review: monthly. Leading.
- Vendor contract coverage. Share of data-handling vendors with updated clauses. Baseline: contract review. Owner: procurement. Review: quarterly. Leading.
- Breach intake time. Hours from detection to data protection lead being informed. Baseline: tabletop exercise. Owner: CISO. Review: half-yearly. Lagging.
Mistakes that cost the most
Starting with a consent tool
A platform bought before the map automates a guess.
- Why it happens: tools are easier to buy than inventories are to build.
- Prevention: finish the map and deletion steps first.
- Early warning: a tool rollout plan with no list of source systems.
Leaving facilities systems out of scope
Parking, Wi-Fi and cameras are rarely on IT's asset list.
- Why it happens: they were bought as building equipment.
- Prevention: include facilities and security in the programme team.
- Early warning: a data map with no entries from the car park.
Assuming vendors carry the obligation
Outsourcing collection does not outsource responsibility.
- Why it happens: contracts predate DPDP.
- Prevention: update contracts and name an internal owner per vendor.
- Early warning: nobody internally can say where vendor data is stored.
Collecting for marketing without saying so
A Wi-Fi login that quietly feeds a campaign list is a notice problem.
- Why it happens: marketing uses whatever data exists.
- Prevention: separate, clearly optional marketing consent.
- Early warning: campaigns sent to numbers captured at the Wi-Fi portal.
Ignoring access logs
Without them, misuse cannot be investigated.
- Why it happens: older recorders do not support named users.
- Prevention: replace or wrap systems that cannot log access.
- Early warning: shared passwords on security consoles.
Frequently asked questions
When do DPDP obligations apply to retailers?
The DPDP Rules were notified in November 2025 with an 18-month phased timeline. Core obligations on notice, consent, security, breach reporting and retention apply from around May 2027. Consent manager registration opens after 12 months.
Does DPDP apply to CCTV footage?
The Act covers digital personal data. Digital footage in which people can be identified is likely to fall within scope, but the exact treatment, including retention, should be confirmed with legal counsel for your premises.
Is a phone number collected for Wi-Fi personal data?
Yes, a mobile number linked to a person is personal data. Collecting it brings notice, security and erasure duties, so check whether the login step needs it at all.
What must a consent notice contain?
It must be standalone, clear and simple, and explain the specific purpose for which personal data is collected and used. Test it on a mobile screen, where most shoppers will see it.
How fast must a breach be reported?
Affected individuals must be informed without delay. A detailed report must reach the Data Protection Board within 72 hours of becoming aware of the breach.
Who is responsible when an agency runs a mall contest?
Generally, the organisation that decides why and how the data is used carries the main obligation. If the mall sets the purpose, the mall is likely responsible even if the agency holds the data. Confirm with counsel.
How long should personal data be kept?
Only as long as its purpose is served, subject to a one-year minimum retention for certain data and logs under the Rules and any longer period required by other laws. Document the period for each flow.
What are the penalties under DPDP?
The Data Protection Board can impose penalties of up to ₹250 crore for certain failures, such as not taking reasonable security safeguards. The actual amount depends on the breach and the Board's assessment.
What to do next
Walk one property this month and build the first collection list before any tool discussion. For how the same evidence-first thinking applies to regulated lending, read gold loan compliance as a data problem, and see the technology governance topic page for the wider framework.
Sources
- Press Information Bureau, DPDP Rules, 2025 notified, November 2025. pib.gov.in
- Press Information Bureau, Digital Personal Data Protection Rules, 2025 explainer, November 2025. pib.gov.in
- Grant Thornton Bharat, DPDP Act and Rules brochure, November 2025. grantthornton.in
- Ikigai Law, A closer look at the DPDP Rules 2025, November 2025. ikigailaw.com
Last reviewed: 15 September 2026.
Views are my own and do not represent my employer.
This article is general information, not legal advice.